

Cyber Crime & Online Fraud in India: UPI Fraud, Bank Fraud, Identity Theft, Hacking, Digital Arrest, Social-Media Offences & Cross-Border Matrimonial Disputes
Adv. Tarun Choudhury
Supreme Court Advocate | 25+ Years of Legal Experience
1. Cybercrime Is No Longer Merely a Technology Problem
When most people hear the words “cybercrime” or “online fraud”, they still picture a hacker sitting behind a computer, breaking into somebody’s system.
That is no longer an accurate picture of the problem.
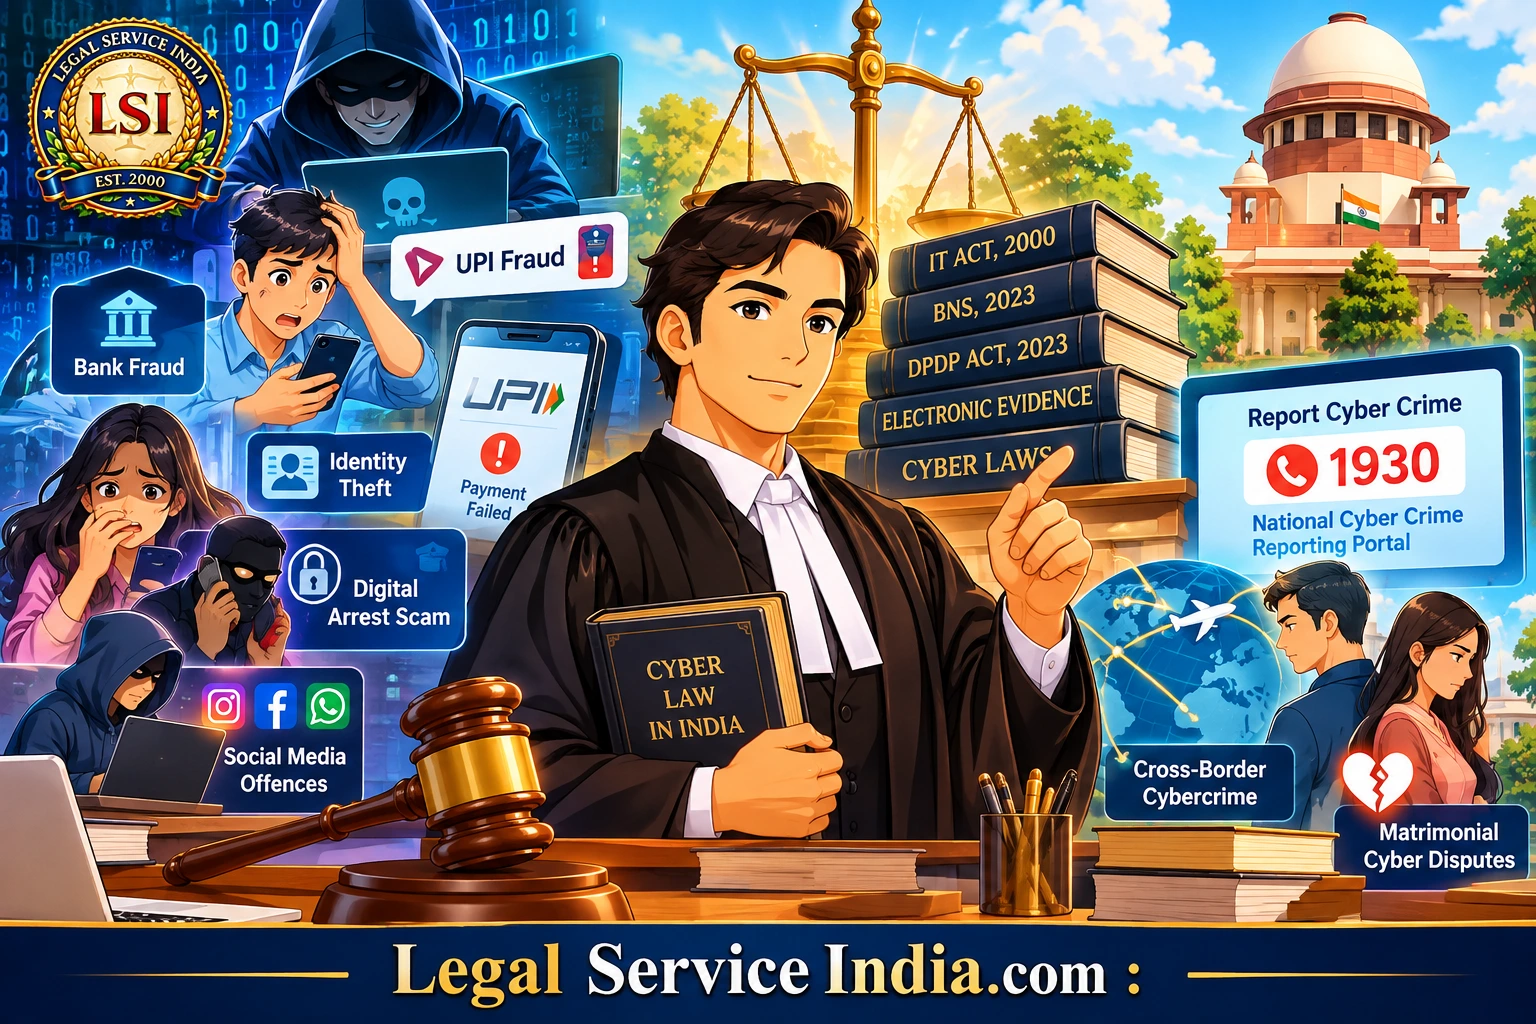
Today, a cybercrime complaint can start with something as ordinary as a telephone call, a WhatsApp message, an apparently genuine communication from a bank, a QR code, a matrimonial dispute, a fake investment application, a video call from somebody claiming to be a police officer, or even a message from a person pretending to be a relative.
The technology involved may be surprisingly simple.
The legal consequences may be anything but simple.
A person may lose money through a UPI transfer, discover that a mobile number has been taken over, find that somebody has entered an email account without permission, come across a fake social-media profile, receive threats involving private photographs, or be coerced into transferring money during what is commonly described as a “digital arrest”.
In every such case, I would begin with a very basic question:
What exactly happened?
The next question is equally important:
What evidence proves it?
Only after those questions have been properly answered should we move to the next level:
Which offence has actually been committed, which authority should be approached, and what remedy is realistically available?
That is the approach I take in serious cybercrime matters.
2. What Is Cyber Crime & Online Fraud?
There is no single offence called “cybercrime”.
The expression covers a wide range of conduct involving computers, communication devices, electronic records, digital accounts, payment systems, networks and online platforms.
Depending upon the facts, a case may involve:
- unauthorised access to a computer or account;
- identity theft;
- cheating by personification;
- fraudulent use of passwords or unique identification features;
- unauthorised electronic transactions;
- social media impersonation;
- online investment fraud;
- UPI fraud;
- bank-account takeover;
- SIM-swap fraud;
- remote-access fraud;
- phishing, vishing or smishing;
- sextortion and digital blackmail;
- publication or transmission of prohibited material;
- cyberstalking or threats;
- digital-arrest scams;
- fake government or court communications;
- ransomware or malware;
- cryptocurrency or virtual-digital-asset fraud;
- matrimonial or relationship-related cyber offences.
The important point is that the law should be selected from the facts, rather than from the terminology used by the complainant.
Calling something “hacking” does not, by itself, establish that hacking has legally occurred. Likewise, describing a transaction as “cyber fraud” does not tell us which statutory provisions actually apply.
The sequence of events has to be reconstructed first.
3. The Principal Laws Applicable in 2026
A modern cybercrime case often requires several legal frameworks to be considered together.
Information Technology Act, 2000
The Information Technology Act continues to be the principal cyber-specific legislation.
Depending upon the facts, provisions that may become relevant include:
- Section 43 — specified unauthorised acts involving computers, systems, networks or data, with civil consequences including compensation;
- Section 66 — certain acts referred to in Section 43 when done dishonestly or fraudulently, attracting criminal consequences;
- Section 66C — identity theft involving fraudulent or dishonest use of specified electronic signatures, passwords or unique identification features;
- Section 66D — cheating by personation using a communication device or computer resource;
- Section 66E — violation of privacy involving capture, publication or transmission of the image of a private area without consent;
- Section 75 — application of the Act to certain offences or contraventions committed outside India where the statutory conditions are satisfied.
This is why I would avoid treating “hacking” as a magic legal word. The conduct has to be mapped to the statutory provision whose ingredients it actually satisfies.
Bharatiya Nyaya Sanhita, 2023
The BNS is equally important where the underlying conduct amounts to a conventional criminal offence committed through digital means.
Section 318 — Cheating
Section 318 defines cheating and provides different punishments depending upon the circumstances.
In a serious online money-fraud case, Section 318(4) may become particularly relevant where cheating dishonestly induces delivery of property.
The distinction between the different subsections matters. A lawyer should therefore not simply write “BNS Section 318” without first examining the precise factual ingredients.
Section 319 — Cheating by Personation
This provision may become relevant where a person cheats by pretending to be somebody else or by knowingly substituting one person for another.
That can arise in cases involving:
- fake bank-officer calls;
- fake police or government-official calls;
- social media impersonation;
- fake customer-care communications;
- identity-based online scams.
Extra-Territorial Conduct
The BNS contains provisions dealing with specified offences committed outside India, including circumstances covered by Section 1(5)(c) involving a computer resource located in India.
The Information Technology Act separately contains Section 75.
There is, however, an important distinction which is often overlooked:
Jurisdiction to investigate or prosecute is not the same thing as the practical ability to arrest a person abroad or obtain evidence held in another country.
That distinction becomes particularly important in NRI and cross-border cases.
4. UPI Fraud: What Should You Do?
UPI has made digital payments extraordinarily convenient. Unfortunately, the same convenience has also created new avenues for fraud.
Common cases include:
- fake customer-care numbers;
- fake refund requests;
- QR code manipulation;
- “receive money” scams;
- fake KYC communications;
- impersonation of relatives or business contacts;
- remote-access applications;
- investment scams;
- fake loan applications;
- fraudulent payment links;
- account takeover following SIM compromise.
There is one misconception about QR codes that deserves particular attention.
A person may be told:
“Scan this QR code and enter your UPI PIN to receive the refund.”
The UPI PIN is ordinarily used to authorise a payment, not merely to receive money.
That simple distinction has prevented many avoidable losses.
If somebody is asking you to enter your UPI PIN in order to “receive” money, you should stop and verify the transaction before proceeding.
5. The First Hour After UPI or Online Banking Fraud
If money has just been transferred fraudulently, do not spend the first hour arguing with the fraudster.
Act.
1. Call 1930
The National Cyber Crime Helpline is available 24×7 for immediate reporting of financial cyber fraud.
Provide, as accurately as possible:
- transaction amount;
- date and time;
- UTR/RRN or transaction reference;
- beneficiary account or UPI ID;
- bank name
- mobile number used;
- screenshots;
- details of the person who contacted you.
2. Immediately Contact Your Bank
Use the bank’s official fraud-reporting channel.
Ask for:
- complaint/reference number;
- immediate action to prevent further unauthorised transactions;
- confirmation that the transaction has been reported as fraudulent/unauthorised;
- appropriate action concerning the beneficiary account where possible.
Do not depend solely upon a telephone conversation. Get a written record wherever possible.
3. File or Complete the NCRP Complaint
The National Cyber Crime Reporting Portal provides separate routes for financial fraud and other cybercrime.
Save the acknowledgement.
4. Secure the Remaining Accounts
If account takeover is suspected:
- change passwords from a trusted device;
- Disable compromised UPI access where appropriate
- block or hotlist compromised cards;
- review other linked accounts;
- remove unauthorised devices;
- Contact the telecom provider if SIM compromise is suspected.
5. Preserve Evidence
Do not delete:
- WhatsApp chats;
- SMS alerts;
- emails;
- call logs;
- transaction messages;
- suspicious APKs;
- screen recordings;
- forged documents;
- caller numbers;
- URLs;
- UPI IDs;
- bank statements.
6. Do Not Factory-Reset the Device
If the phone itself may contain evidence, wiping it can destroy information that investigators or forensic specialists may later need.
7. Do Not Pay a “Recovery Agent”
After a fraud, victims are often approached by people claiming that they can recover the money if another payment is made.
Treat such claims with extreme caution.
If somebody tells you:
“Pay another amount to unlock your account.”
or:
“Pay to speak to the judge or police officer on the video call.”
Do not make the payment simply because the caller sounds official.
6. What Does 1930 Actually Do?
The 1930 system is important because, in financial cyber fraud, time can make a real difference.
A complaint can feed into the cyber-fraud response mechanism, including efforts to identify and restrict the movement of funds through beneficiary accounts.
The practical distinction is this:
| Issue | What It Means |
|---|---|
| Reporting a fraud | Initiating the appropriate reporting and response process. |
| Recovering the money | A separate legal and operational question that depends on the facts and the movement of funds. |
Reporting a fraud and recovering the money are two different legal and operational questions.
The earlier a victim reports the transaction, the greater the practical opportunity may be to intercept money before it is moved through several accounts.
But no responsible lawyer should tell a victim:
“Call 1930, and your money will definitely come back.”
That is not a promise that the system can lawfully or realistically make.
7. Mule Accounts: Why the Money May Disappear Quickly
Online fraudsters frequently do not receive stolen money directly into their own personal accounts.
Instead, the money may move through a chain such as the following:
Victim → first beneficiary → second account → third account → cash withdrawal / wallet / other financial channel
The first beneficiary may be a mule account, rather than the person ultimately organising the fraud.
That is one reason why the first response can matter more than producing an elegantly drafted FIR several days later.
The investigation may need to trace:
- account-opening information;
- KYC details;
- transaction history;
- UPI identifiers;
- device information;
- IP logs;
- mobile numbers;
- ATM withdrawals;
- CCTV;
- subsequent transfers;
- linked accounts.
A suspect account identifier may also be reported through the NCRP’s Report Suspect facility.
The portal currently permits reporting of identifiers, including website URLs, WhatsApp numbers/Telegram handles, telephone numbers, email IDs, SMS headers/numbers and social media URLs.
The NCRP also provides a Suspect Repository through which identifiers can be searched.
But a repository entry should never be treated as proof that a person is guilty. It is a complaint/information-based investigative facility, not a judicial finding.
8. Digital Arrest and Impersonation of Police, ED, CBI or Courts
One of the more serious developments in online fraud has been the so-called digital arrest scam.
The person on the other side may claim to be:
- a police officer;
- CBI officer;
- ED official;
- customs officer
- Supreme Court or High Court official;
- judicial authority;
- bank or regulatory officer.
The victim may be told that:
- A SIM card has been used in a crime
- A bank account is connected with money laundering
- A parcel contains illegal material
- An arrest warrant has been issued
- The person’s Aadhaar/PAN has been misused;
- the person’s property will be seized.
The fraudster may then move the victim to a video call and display forged documents, uniforms, seals, court papers or identification cards.
The Supreme Court has taken suo motu cognisance of such scams in In Re: Victims of Digital Arrest Related to Forged Documents, SMW (Crl.) No. 3/2025.
The proceedings arose from complaints in which fraudsters impersonated police, investigating agencies and judicial authorities, used forged official documents, and coerced victims — including senior citizens — into transferring money.
The Court has subsequently issued interim directions concerning coordinated investigation, mule accounts, SIM misuse, grievance redressal and restoration of defrauded money. These measures form part of an evolving institutional response; they do not amount to a private guarantee of refund in an individual case.
If you are confronted with such a scam:
- Do not transfer money merely because the caller threatens arrest.
- Preserve the documents and communications, and immediately report the financial transaction and cyber offence through the appropriate official channels.
9. Bank Fraud and Unauthorised Electronic Transactions
This is one area where legal advice is often made far too simplistic.
Two statements are both wrong:
“The bank must refund every fraudulent transaction.”
And:
“You entered the OTP, so the bank has no responsibility.”
Neither proposition is universally correct.
The central RBI framework remains the 6 July 2017 Customer Protection – Limiting Liability of Customers in Unauthorised Electronic Banking Transactions, RBI/2017-18/15, DBR.No.Leg.BC.78/09.07.005/2017-18.
The framework broadly distinguishes between:
- bank negligence/contributory fraud/deficiency;
- third-party breach where neither bank nor customer is at fault;
- customer negligence.
Under the RBI framework, customer liability can depend significantly on when the customer reports the unauthorised transaction after receiving the bank’s communication.
For a qualifying third-party breach, notification within three working days can result in zero customer liability.
A delay of four to seven working days can attract the limited-liability structure specified in the circular, while liability beyond seven working days is governed by the bank’s Board-approved policy.
Where the loss is attributable to customer negligence, such as sharing payment credentials, the customer may bear the loss until the transaction is reported; subsequent loss after reporting is dealt with differently under the framework.
The RBI framework provides for shadow reversal within 10 working days from notification by the customer in qualifying zero- or limited-liability cases, without waiting for settlement of an insurance claim.
The bank must also resolve the complaint and establish customer liability within the period specified in its Board-approved policy, subject to the circular’s outer framework.
The burden of proving customer liability lies on the bank.
The practical point is therefore this:
The presence of an OTP, UPI PIN or other authentication factor is an important fact, but it does not by itself answer every question concerning authorisation, deception, bank systems, customer negligence, third-party breach or liability.
The entire transaction sequence has to be examined.
10. A Difficult but Important Distinction: Deceived Payment vs Unauthorised Payment
Suppose A secretly obtains B’s banking credentials and transfers ₹10 lakh without B knowing anything.
That is a straightforward unauthorised-transaction scenario for investigation.
Now change the facts.
Suppose A impersonates a bank official and persuades B to enter a UPI PIN and approve a payment of ₹10 lakh.
The second case raises a more complicated question concerning how the payment was authorised, how the fraud occurred, what the bank’s systems detected, what information was supplied to the customer, and how the RBI customer-liability framework applies to those facts.
That is precisely why a responsible lawyer should not promise:
“The bank will definitely refund your money.”
The proper question is:
How should the transaction be legally classified, and what evidence supports that classification?
11. If the Bank Says No: Escalation and RBI Ombudsman
A victim should not necessarily stop after receiving a rejection from the bank.
A sensible escalation pathway may involve:
- Bank fraud/reporting channel
- Written grievance
- Bank’s internal escalation mechanism
- RBI Ombudsman framework where maintainable
- Appropriate civil/criminal remedies
The Reserve Bank – Integrated Ombudsman Scheme, 2026 (RB-IOS 2026) came into force on 1 July 2026.
The scheme provides a cost-free grievance-redress mechanism for eligible complaints concerning deficiency in service by covered regulated entities.
There is an important procedural point here: the complainant should first approach the concerned regulated entity.
Under the RB-IOS 2026 framework, a complaint may ordinarily be taken to the RBI Ombudsman where the regulated entity has not replied within the applicable period, including the prescribed 30-day period where applicable, or where the complainant is dissatisfied with the response or resolution. The complaint remains subject to the scheme’s other maintainability requirements and time limits.
The RBI’s CMS portal is the principal online route.
The Ombudsman process should not be confused with a criminal investigation.
A bank-liability dispute and a criminal cybercrime investigation can proceed on different tracks.
12. Identity Theft: Section 66C IT Act
Section 66C of the Information Technology Act deals with fraudulent or dishonest use of specified electronic signatures, passwords or unique identification features belonging to another person.
It can become relevant where, for example:
- A password is stolen and used;
- A unique identification feature is misused;
- An account is taken over using stolen credentials
- An electronic identity is fraudulently used.
But not every fake photograph or fake social media profile should automatically be labelled a Section 66C offence.
The exact statutory ingredients matter.
Depending upon the facts, other provisions such as Section 66D of the IT Act, BNS Section 319 and other provisions may also be relevant.
Charging discipline matters.
13. Online Cheating and Personation
Online fraud often combines conventional cheating with digital technology.
For example:
A fraudster pretends to be a bank employee, convinces the victim that the victim’s account is under investigation, obtains confidential information and induces a transfer.
Depending on the evidence, the investigation may involve:
- BNS Section 318;
- BNS Section 319;
- IT Act Section 66D;
- Identity-theft provisions;
- Forgery-related offences where forged documents were used;
- Other provisions depending upon the precise conduct.
The FIR should describe the actual conduct, rather than simply saying:
“I was cyber cheated.”
The more accurately the transaction sequence is reconstructed, the easier it becomes to identify which legal provisions are genuinely attracted.
14. Hacking and Unauthorised Access
“Hacking” is commonly used as an umbrella expression.
Legally, however, the analysis may involve several different provisions.
Section 43 of the IT Act
Section 43 covers specified unauthorised acts relating to computers, computer systems, networks and data.
Section 66 IT Act
Where the relevant acts under Section 43 are done dishonestly or fraudulently, Section 66 can bring criminal consequences.
Section 66C
This may apply where passwords or specified unique identification features are fraudulently or dishonestly used.
Section 66D
This concerns cheating by personification using a communication device or computer resource.
The Evidence May Include
- Login records;
- IP addresses;
- Device IDs;
- Security alerts;
- Password-reset records;
- Two-factor authentication records;
- Email headers;
- Server logs;
- Browser information;
- Forensic examination;
- Telecom records.
The word “hacked” is not a substitute for proving what happened technically.
15. SIM-Swap and Mobile-Number Takeover
A SIM-swap case requires immediate parallel action.
The victim may discover that:
- The original SIM has suddenly stopped working;
- A replacement SIM has been activated
- OTPs are no longer reaching the victim
- Banking transactions begin shortly afterwards.
The response should potentially involve:
- Bank
- Telecom provider
- 1930/NCRP
- Preservation of evidence
Relevant Evidence May Include
- SIM replacement records;
- Activation/deactivation records;
- Subscriber details;
- Call-detail records where lawfully obtainable;
- Device information;
- Bank login records;
- OTP delivery records;
- Transaction logs.
The fact that an OTP was successfully used after a SIM takeover does not, by itself, answer the question of who authorised the transaction.
The technical sequence matters.
16. Remote-Access Applications and Screen-Sharing Fraud
Another recurring pattern involves applications that permit remote access or screen sharing.
A victim may be instructed to download an application supposedly for:
- Customer support;
- Refund processing;
- KYC verification;
- Technical assistance;
- Bank support.
Once installed, the fraudster may be able to observe or manipulate the device.
The legal and banking significance of that fact can be substantial.
The Investigator Should Ask
- Who instructed the victim to install the application?
- What exactly was the victim told?
- What permissions were granted?
- Was screen sharing activated?
- Was the application subsequently used to access banking applications?
- What transactions occurred?
- What device was used?
- What logs remain?
Again, the objective is not to blame the victim.
The objective is to reconstruct the sequence accurately.
17. Social-Media Impersonation, Sextortion and Digital Blackmail
Cybercrime increasingly intersects with personal and social relationships.
A person may create a fake profile in another person’s name, contact relatives, demand money, threaten publication of private photographs, or use intimate material to coerce the victim.
Potentially relevant provisions will depend on the precise facts and may include:
- IT Act provisions;
- BNS provisions relating to cheating, personation, threats or other offences;
- Section 66E, where its specific statutory ingredients are satisfied;
- Provisions relating to obscene or sexually explicit electronic material where applicable.
Here again, the evidence may matter more than the label.
Preserve
- Original messages;
- Profile URLs;
- Usernames;
- Account IDs;
- Timestamps;
- Screenshots;
- Downloaded files;
- Call recordings where lawfully obtained;
- Emails;
- Payment demands.
Do not edit screenshots before preserving the original material.
And in sextortion cases, sending more money does not solve the underlying problem simply because the offender promises to delete the material.
18. Section 66A Is Not Law
This point deserves a separate heading because outdated cyber-law articles continue to cite Section 66A.
The Supreme Court struck down Section 66A of the Information Technology Act in:
Shreya Singhal v. Union of India, (2015) 5 SCC 1.
Section 66A therefore cannot be cited as an operative criminal provision merely because it continues to appear in old copies or outdated articles of the statute.
If a 2026 cyber-law article casually advises a client to proceed under Section 66A, that is a serious quality-control problem.
19. Electronic Evidence Under the Bharatiya Sakshya Adhiniyam, 2023
This is perhaps the most important part of the discussion for lawyers dealing with modern cybercrime.
The Bharatiya Sakshya Adhiniyam, 2023 (BSA) governs electronic evidence under the current statutory framework, subject to its commencement and transitional provisions.
Sections 61, 62 and 63 are central to electronic records.
Section 61 recognises electronic and digital records as having the same legal effect, validity and enforceability as other documents, subject to Section 63.
Section 62 provides that the contents of electronic records may be proved in accordance with Section 63.
Original Electronic Record and Computer Output Are Not the Same Thing
This distinction is crucial.
An original electronic record may exist on:
- A mobile phone;
- A computer;
- A storage device;
- A server;
- Another electronic system.
A screenshot, printout or other computer output may be a reproduction of information contained in such a system.
The route by which the evidence is produced therefore matters.
Section 63 Certificate
Section 63(4) provides for a certificate accompanying electronic evidence when it is sought to be admitted through the statutory computer-output route.
The certificate is prescribed in the Schedule to the BSA and contains Part A and Part B.
Part A concerns the party/person producing the electronic record or output and the relevant device or digital-record source.
Part B concerns certification by an expert.
The schedule requires disclosure of hash value(s) and a hash report, together with the prescribed certification requirements concerning the electronic record and device.
The statutory framework therefore treats the hash value as part of the certification exercise rather than as a mere forensic embellishment.
The certificate is to be signed by the person responsible for the relevant device/activities and by the expert contemplated by the statutory scheme.
This is why a cybercrime lawyer should not simply print a WhatsApp conversation and say:
“This is the evidence.”
A screenshot may be extremely useful as an investigative lead.
But the court may still have to consider:
- Where the original information resides;
- How the copy was generated;
- Who controlled the device
- Whether the record is complete;
- Whether it has been altered;
- Whether the applicable certificate is required;
- Whether technical evidence is necessary;
- Whether the opposing party disputes authenticity.
Arjun Panditrao Khotkar
The leading Supreme Court authority remains:
Arjun Panditrao Khotkar v. Kailash Kushanrao Gorantyal, (2020) 7 SCC 1.
That judgement interpreted Section 65B of the now-repealed Indian Evidence Act and held that the statutory certificate requirement applied to the relevant form of secondary electronic evidence.
The judgement remains important in understanding the distinction between original electronic evidence and computer output.
But a 2026 article must not make the mistake of saying:
“Section 65B is the current law.”
It is not.
The present statutory framework is the BSA, particularly Sections 61–63.
Pune Bar Association and the New Section 63 Framework
The Supreme Court has also considered the new Section 63 framework in 2026. In Pune Bar Association v. Union of India, W.P.(C) No. 599/2026, the Court declined to treat the Section 63(4) certification requirements as unconstitutional and discussed the Schedule’s Part A/hash and Part B/expert structure. The Court also clarified that the issue of whether only an Examiner of Electronic Evidence under Section 79A of the IT Act can sign Part B was not conclusively decided; that question of law was left open.
That order should therefore not be overstated as a comprehensive ruling on every issue concerning Section 63.
Transitional Cases
There is another point practitioners should not overlook.
The BSA contains savings provisions concerning proceedings that were already pending when the new law commenced.
The applicable evidence statute must therefore be checked with reference to the procedural history of the particular case.
A lawyer should not mechanically apply BSA Section 63 to every old proceeding merely because the case is being heard in 2026.
20. Preserve the Device — Do Not Destroy the Evidence
In a serious cybercrime matter, the device itself may be evidence.
That can include:
- Mobile phone;
- Laptop;
- Tablet;
- Hard drive;
- SIM card;
- Router;
- Storage device.
If a phone is potentially compromised, the natural temptation is to reset it.
That may be precisely the wrong thing to do.
Depending upon the circumstances, forensic preservation may involve:
- Imaging;
- Extraction;
- Hash calculation;
- Metadata preservation;
- Examination of application artefacts;
- Login history;
- Deleted material;
- Device logs;
- Communication records.
The precise forensic method should be determined by the investigating authority or a qualified forensic professional.
The principle is simple:
Do not destroy the evidence while trying to clean the device.
21. WhatsApp Evidence: Useful Does Not Mean Automatically Proved
WhatsApp messages can be important evidence.
But there are several separate questions to consider:
| Question |
|---|
| Does the account belong to the person alleged? |
| Who actually operated the device? |
| Has the message been altered? |
| Is the conversation complete? |
| What device contains the underlying record? |
| Is the message an original electronic record or a computer output? |
| Is certification required for the method by which the evidence is being tendered? |
| Can the sender and recipient be independently established? |
| Does the message prove the fact alleged, or merely show that the message existed? |
A WhatsApp screenshot is therefore not worthless.
But neither is it automatically conclusive.
22. Cybercrime and Matrimonial Disputes
This is an area where I would urge particular caution.
A husband and wife may have:
- shared devices;
- shared passwords;
- joint bank accounts;
- family email accounts;
- common financial arrangements;
- access to each other’s phones;
- jointly used computers.
A dispute may later arise over money, photographs, emails, social media accounts or messages.
At that stage, one party may say:
“My spouse hacked me.”
The other may respond:
“We always shared that password.”
Neither statement should automatically decide the legal character of the dispute.
The first question should be:
What was the actual authority to access the account at the relevant time?
Historical password sharing can be relevant evidence.
But a password that was once shared does not necessarily establish unlimited authority forever, particularly after separation or withdrawal of permission.
Conversely, the absence of a formal written power of attorney does not automatically turn every act occurring within a previously shared household into a cyber offence.
The facts have to be examined carefully.
23. Genuine Cybercrime or Matrimonial Dispute Wearing a Cyber Label?
This distinction can be critical.
A matrimonial court deals with matrimonial rights and relief.
A criminal investigation deals with alleged offences.
A bank’s fraud department deals with banking transactions.
These forums perform different functions.
A divorce proceeding does not automatically determine whether a computer was unlawfully accessed.
A cyber FIR does not automatically determine who is entitled to matrimonial property.
A dispute over a genuine joint bank account does not automatically become hacking.
Indicators that may point toward a genuine cyber offence
For example:
- an unexplained new-device login;
- a SIM replacement that the account holder did not authorise;
- password-reset activity;
- transfers to unrelated third-party accounts;
- remote-access software installed through deception;
- fake profiles created in the victim’s name;
- forged official documents;
- Account access after permission was clearly withdrawn.
Indicators that may point toward a matrimonial/property dispute
For example:
- long-standing joint-account operating instructions;
- established family practice concerning withdrawals;
- historic shared credentials;
- transactions consistent with earlier household arrangements;
- no identifiable technical intrusion;
- allegations arising only after matrimonial litigation began.
Neither list is conclusive.
The evidence must determine the legal character of the dispute.
The wrong approach is to file a hacking complaint merely as leverage over maintenance or matrimonial property.
The equally wrong approach is to dismiss a genuine account takeover simply because the alleged offender happens to be the victim’s spouse.
24. The Cross-Border Matrimonial Cybercrime Problem
This is becoming increasingly important for Indian families with international connections.
Consider a hypothetical situation.
An Indian spouse is living in India.
The other spouse is living in the United States, United Kingdom, UAE or another foreign jurisdiction.
There is a matrimonial dispute.
The Indian spouse alleges that:
- The overseas spouse accessed an Indian email account
- A SIM was duplicated or replaced;
- Money was transferred from an Indian bank account
- WhatsApp messages were obtained;
- Social media accounts were accessed;
- Relatives received threatening communications;
- The foreign spouse used information obtained from the account during divorce proceedings.
The foreign spouse says:
“We always shared passwords and accounts.”
The matter is no longer simply a cybercrime problem.
It may involve at least four separate jurisdictional questions.
1. Matrimonial jurisdiction
- Where is the divorce or matrimonial proceeding pending?
- Which personal law applies?
- Where did the parties last reside together?
- Where was the marriage solemnised?
- Where does the respondent reside?
2. Criminal jurisdiction
- Where did the alleged unauthorised access occur?
- Where was the victim located?
- Where was the computer resource located?
- Where did the financial loss occur?
- Do BNS Section 1(5)(c) or the IT Act Section 75 apply?
3. Banking jurisdiction
- Which bank holds the account?
- Was it a sole or joint account?
- What was the operating mandate?
- Which payment system processed the transaction?
- Where is the beneficiary bank?
4. Evidence jurisdiction
- Where are the devices?
- Where are the servers?
- Where are the cloud records?
- Where is the platform provider located?
- Where is the foreign bank?
These questions are connected, but they are not the same question.
25. Foreign Evidence: What a Lawyer Can and Cannot Promise
Suppose relevant evidence is held by a foreign platform or foreign bank.
A lawyer’s demand letter may be useful for preservation.
But a letter saying:
“Please send us the complete account contents immediately.”
does not necessarily compel a foreign service provider to produce the evidence.
Depending upon the country, the evidence and the applicable legal mechanism, the matter may require:
- preservation requests
- formal judicial process;
- production orders;
- requests through competent authorities;
- mutual legal assistance mechanisms;
- other recognised international cooperation procedures.
Similarly, if money has reached a foreign bank, Indian criminal jurisdiction does not automatically mean that the foreign bank will freeze the account simply because an Indian advocate sends an email.
The correct advice is to explain the process — not to promise an outcome.
26. Civil and Criminal Remedies May Exist Together
A cybercrime victim may require more than an FIR.
Depending upon the facts, the legal strategy may involve several tracks.
Criminal remedies
- cybercrime complaint;
- FIR/investigation;
- seizure and forensic examination;
- identification of beneficiaries;
- investigation of account trails;
- prosecution under applicable statutory provisions.
Banking remedies
- fraud reporting;
- reversal or dispute processes where the payment system permits them;
- grievance escalation;
- RBI Ombudsman mechanism where maintainable.
Civil remedies
- injunction;
- preservation orders;
- recovery proceedings;
- protection against further dissemination;
- appropriate orders concerning specific assets or proceeds.
Matrimonial remedies
Where the dispute is genuinely matrimonial, the appropriate family/matrimonial court may also need to deal with:
- maintenance;
- matrimonial property issues;
- custody;
- disclosure;
- financial records;
- related relief.
The remedies should be coordinated rather than indiscriminately combined.
27. What Information Should a Cybercrime Lawyer Ask For?
Before advising a client, I would want a clear chronology.
At a minimum:
About the incident
- Date and exact approximate time
- First contact
- Phone number/email/WhatsApp account
- What was represented
- What the victim did
- What the accused did
- Amount involved
About the financial transaction
- Bank name
- Account type
- UPI ID
- UTR/RRN
- Beneficiary account
- Transaction date/time
- Number of transactions
- Whether OTP/PIN was entered
- Whether the transaction was manually authorised
- Whether the customer received an alert
About the device
- Phone model
- SIM status
- Recent SIM replacement
- Applications installed
- Remote-access software
- Login alerts
- Password changes
- Security notifications
About the evidence
- Screenshots
- Original chats
- Emails
- Call records
- Bank statements
- Transaction receipts
- URLs
- Profile links
- Documents sent by the fraudster
- Device itself
About jurisdiction
- Victim’s location
- Accused’s location
- Bank location
- Beneficiary location
- Device location
- Platform/provider location
In matrimonial cases
- Date of marriage
- Place of residence
- Separation date
- Existing divorce proceedings
- Previous password sharing
- Joint accounts
- Separate accounts
- Existing injunctions or court orders
- Whether the alleged access occurred before or after separation
Without this information, cybercrime advice is often little more than guesswork.
28. The First 60 Minutes: A Practical Checklist
If the fraud has just occurred:
- 1. Call 1930.
- 2. Contact the bank through its official fraud channel.
- 3. Obtain complaint/reference numbers.
- 4. Ask for immediate preventive action concerning further transactions.
- 5. Preserve the UTR/RRN and beneficiary details.
- 6. Secure UPI, cards, email and other accounts.
- 7. Contact the telecom operator immediately if SIM-swap is suspected.
- 8. Preserve WhatsApp, SMS, email, call logs and screenshots.
- 9. Do not factory-reset the device.
- 10. Do not uninstall potentially relevant applications before preserving evidence unless instructed by the appropriate technical investigator.
- 11. File/complete the NCRP complaint and save the acknowledgement.
- 12. Report suspicious identifiers through the NCRP Report Suspect facility where appropriate.
- 13. Write down the entire sequence while it is still fresh.
- 14. Do not send additional money to “recover” the original money.
- 15. Take legal advice promptly where the amount is substantial, the accused is abroad, the bank has rejected liability, a spouse is involved, the identity is still being misused, or significant electronic evidence is at risk.
29. Common Mistakes Victims Should Avoid
Mistake 1: Waiting several days
Delay can make financial tracing more difficult.
Mistake 2: Deleting the chats
The conversation may be important evidence.
Mistake 3: Resetting the phone
This can interfere with forensic preservation.
Mistake 4: Relying only on the FIR
A complaint is only one part of the response.
Bank records, transaction trails and technical evidence may be equally important.
Mistake 5: Believing every recovery agent
Fraud victims are often targeted again.
Mistake 6: Using outdated law
Section 66A is a classic example.
Mistake 7: Filing every conceivable section
A kitchen-sink FIR is not necessarily a stronger FIR.
Mistake 8: Treating screenshots as automatically conclusive
Electronic evidence must be proved through the legally appropriate route.
Mistake 9: Treating every matrimonial disagreement as hacking
A financial dispute is not automatically cybercrime.
Mistake 10: Promising recovery of money
No lawyer can responsibly guarantee recovery merely because an NCRP complaint or FIR has been filed.
30. Important Supreme Court Authorities
Anvar P.V. v. P.K. Basheer
(2014) 10 SCC 473
Important historical authority on electronic evidence and the special statutory procedure under the former Evidence Act.
Arjun Panditrao Khotkar v. Kailash Kushanrao Gorantyal
(2020) 7 SCC 1
Important Supreme Court authority on the former Section 65B certificate regime and the distinction between original electronic evidence and computer output.
For 2026 practice, its reasoning must be read alongside BSA Sections 61–63, rather than cited as though Section 65B remains the operative statutory provision.
Shreya Singhal v. Union of India
(2015) 5 SCC 1
Section 66A of the Information Technology Act was struck down.
K.S. Puttaswamy v. Union of India
(2017) 10 SCC 1
Foundational constitutional authority recognising privacy as a fundamental right. It provides important constitutional background for digital privacy but is not itself a charging provision under the IT Act.
In Re: Victims of Digital Arrest Related to Forged Documents
SMW (Crl.) No. 3/2025
Important current Supreme Court proceedings concerning digital-arrest scams, forged official documents, cyber-fraud proceeds and coordinated institutional response.
The Supreme Court’s 4 August 2026 order records continuing directions concerning CBI investigation, mule accounts, SIM misuse, grievance redressal and restoration of defrauded money.
Pune Bar Association v. Union of India
W.P.(C) No. 599/2026, order dated 22 May 2026
Relevant to the developing judicial discussion around BSA Section 63(4), the Schedule, hash values and expert certification.
The Court did not finally decide every question concerning who may sign Part B of the Schedule. In particular, it left open the broader question concerning whether an expert must necessarily be an examiner of electronic evidence notified under Section 79A of the IT Act.
31. Cybercrime Is Often a Combination of Offences
A single incident may involve several different legal elements.
For example:
- Fake police officer + forged court order + video call + threat of arrest + UPI transfers
- may involve:
- personation;
- cheating;
- forgery-related offences;
- electronic evidence;
- banking fraud;
- cybercrime investigation.
Similarly:
- Password theft + unauthorised email access + extraction of private information + impersonation
- may involve:
- unauthorised access;
- identity theft;
- personation;
- privacy-related offences;
- conventional criminal offences depending on the facts.
The job of the lawyer is not to make the FIR look impressive.
It is to identify the actual conduct and build the evidence around it.
32. Cybercrime, Divorce and NRI Families: A Separate Legal Strategy
For an NRI or cross-border matrimonial dispute, I would normally separate the matter into four files.
| File | Legal Area | Issues Covered |
|---|---|---|
| File 1 — Matrimonial | Matrimonial | Divorce, maintenance, custody, matrimonial property and related proceedings. |
| File 2 — Cybercrime | Cybercrime | Unauthorised access, impersonation, identity theft, threats or digital coercion. |
| File 3 — Banking | Banking | Unauthorised transactions, joint/separate accounts, mandates and bank liability. |
| File 4 — Evidence | Evidence | Devices, WhatsApp, email, cloud accounts, foreign platforms, bank records and forensic material. |
Keeping these questions separate at the beginning often prevents the case from becoming unnecessarily confused.
The same facts may eventually overlap.
But the remedies do not automatically overlap.
33. My Approach to a Serious Cybercrime Complaint
I do not begin with:
“Which section should we put in the FIR?”
I begin with:
What happened from the first contact until the last transaction or unauthorised access?
Then I ask:
- Who contacted whom?
- What representation was made?
- What did the victim believe?
- What action did the victim take?
- What did the computer/device actually record?
- Where did the money move?
- Who controlled the relevant account?
- Was there consent, and if so, what was the scope of that consent?
- Was the account or device subsequently accessed without permission?
- What evidence can independently establish the sequence?
That approach becomes particularly important where cybercrime allegations arise in divorce and matrimonial proceedings.
A genuine cyber offence should be investigated as such.
A matrimonial property dispute should not be artificially converted into a hacking case.
And a genuine account takeover should not be dismissed merely because the alleged offender is a spouse or former spouse.
34. Frequently Asked Questions
What Should I Do Immediately After UPI Fraud?
Call 1930, notify the bank through its official fraud channel, preserve the UTR/RRN and transaction evidence, secure the remaining accounts, and file the NCRP complaint.
Does the Bank Have to Refund an Unauthorised UPI Transaction?
Not automatically. Bank liability depends upon the facts and the applicable RBI framework, including whether the case involves bank deficiency, third-party breach or customer negligence and when the transaction was reported.
If I shared an OTP, have I automatically lost my legal case?
No such blanket conclusion should be drawn merely from the existence of an OTP. The entire transaction sequence, deception, device/SIM circumstances, bank systems and applicable RBI framework must be examined.
What Is a Digital Arrest Scam?
It is a fraud in which criminals impersonate police, investigating agencies, courts or other authorities and use threats, forged documents or video calls to coerce victims into transferring money or disclosing information.
Is 1930 a refund helpline?
It is an important cyber-fraud reporting mechanism. It does not itself create a legal guarantee that money will be refunded.
Can WhatsApp Messages Be Used as Evidence in Court?
Yes, electronic communications can be relevant evidence, but their admissibility and proof depend on the applicable evidentiary framework, the manner in which the record is produced, authenticity and the requirements of the BSA.
Is a Screenshot Enough to Prove a WhatsApp Conversation?
Not necessarily. A screenshot may be useful evidence, but questions concerning authenticity, source, completeness and the applicable statutory proof requirements may arise.
Is Section 66A Still Applicable?
No. Section 66A was struck down by the Supreme Court in Shreya Singhal v. Union of India.
Is Accessing My Spouse’s Email Automatically a Cybercrime?
Not automatically. The facts concerning authority, permission, access method, timing, passwords, devices and the nature of the conduct have to be examined under the applicable law.
Can I file a cybercrime complaint in India if the accused is abroad?
Potentially, depending upon the facts and statutory jurisdictional provisions. But Indian jurisdiction does not automatically mean that the foreign person or foreign-held evidence can be obtained immediately.
What if the money has already moved to another bank account?
Report it immediately. The investigation may trace the beneficiary and subsequent accounts. Speed matters because funds may be moved through several layers.
What Is a Mule Account?
It is an account used to receive or move money on behalf of a fraud network. The account holder may be involved knowingly or may have been recruited or deceived.
What Is RB-IOS 2026?
The Reserve Bank – Integrated Ombudsman Scheme, 2026, is an RBI grievance-redress mechanism for eligible complaints concerning deficiency in service by covered regulated entities. It came into force on 1 July 2026.
Can Cybercrime and Divorce Proceedings Exist at the Same Time?
Yes. A matrimonial proceeding and a criminal cybercrime investigation address different legal questions. The existence of one does not automatically determine the outcome of the other.
35. Final Word
Cybercrime litigation is rarely solved by knowing the largest possible number of statutory sections.
It is solved by reconstructing the facts accurately and then building the legal case around those facts.
A serious case may require coordination between:
- the victim;
- the bank;
- the cybercrime authorities;
- the telecom provider;
- forensic specialists;
- the investigating officer;
- matrimonial counsel;
- civil counsel;
- foreign lawyers;
- foreign service providers;
- and, where necessary, international evidence mechanisms.
The central questions remain simple:
- What happened?
- What can be proved?
- Where is the evidence?
- Where did the money go?
- Which law actually applies?
- Which remedy is capable of producing a practical result?
That, ultimately, is the difference between merely filing a cybercrime complaint and developing a proper legal strategy.
Need Legal Assistance in a Cyber Crime or Online Fraud Matter?
Adv. Tarun Choudhury
Supreme Court Advocate | 25+ Years of Legal Experience
If you or a family member has suffered UPI fraud, bank fraud, identity theft, hacking, account takeover, social media impersonation, digital blackmail, digital arrest fraud or an online financial scam, the first priority should be to preserve the evidence and understand the legal position before taking further action.
Particular care is required where the matter involves:
- a substantial financial loss;
- refusal by the bank to accept liability;
- an NRI or foreign accused;
- a foreign bank or online platform;
- matrimonial or divorce proceedings;
- unauthorised access to email or social-media accounts;
- SIM-swap or account takeover;
- forged court/government documents;
- sextortion or threats;
- disputed electronic evidence.
Call / WhatsApp: 9881244487
Email: [email protected]
Important Disclaimer
This article is intended for general legal information and does not constitute legal advice for any particular case. Cybercrime, banking liability, electronic evidence and cross-border jurisdiction are highly fact-specific. The applicable law, procedural position and available remedies should be examined on the facts and documents of the individual matter.
Primary-Source Verification for the Final Copy
The corrections above are supported by the official/primary material checked. The BSA Schedule expressly provides Part A, including device/source information and hash values/hash report, and the Supreme Court’s May 2026 Pune Bar Association order discusses the Part A/Part B structure and the expert-signature issue.
The RBI’s 6 July 2017 circular specifies the three-working-day, four-to-seven-working-day and beyond-seven-working-day liability framework and expressly provides for shadow reversal within 10 working days after customer notification.
The Supreme Court’s 4 August 2026 order in In Re: Victims of Digital Arrest Related to Forged Documents confirms the continuing proceedings concerning digital-arrest scams and directions relating to mule accounts, SIM misuse, grievance redressal and restoration of defrauded money.
The NCRP currently confirms 1930 as the 24×7 financial-cyber-fraud helpline, and its official portal provides both Report Suspect and Suspect Repository facilities, with an express warning that repository entries are complaint-based and are not certified findings of guilt.
Finally, RBI’s official RB-IOS 2026 FAQ confirms that the scheme came into force on 1 July 2026, requires the complainant ordinarily to approach the regulated entity first, and provides the CMS route for eligible complaints.
I have deliberately not compressed the legal substance or removed sections merely to make the article “sound human”. The main change is that the prose now reads more like a senior advocate explaining a live legal problem—more direct, less repetitive, and less mechanically structured—while retaining the article’s original information architecture and substantive coverage.
Key Takeaways
- Cyber Crime & Online Fraud Is Not a Single Offence. The legal response depends on what actually happened, how the transaction or access took place, what evidence is available, and where the people, accounts, devices and data are located.
- UPI fraud, bank fraud, identity theft, hacking, personation, social-media impersonation, sextortion and digital-arrest scams may attract different provisions of the Information Technology Act, 2000, the Bharatiya Nyaya Sanhita, 2023 (BNS) and other applicable laws.
- The 1930 National Cyber Crime Helpline and the National Cyber Crime Reporting Portal (NCRP) are important first-response mechanisms in cases of financial cyber fraud. They are not, however, automatic refund mechanisms.
- A fraudulent debit does not automatically mean that the bank is legally required to refund the money. Bank liability has to be examined under the applicable RBI framework, including the circumstances in which the transaction took place, the customer’s conduct and the time at which the transaction was reported.
- The Bharatiya Sakshya Adhiniyam, 2023 (BSA) now governs electronic evidence. Sections 61–63 are particularly important, and lawyers must carefully distinguish between an original electronic record and a computer output generated from an electronic system.
- Section 66A of the Information Technology Act is not a valid offence. The Supreme Court struck it down in Shreya Singhal v. Union of India.
- In matrimonial disputes, a cybercrime allegation should not automatically be treated as a hacking case simply because the parties are spouses. At the same time, marriage does not give either spouse a blanket licence to access the other person’s accounts, devices or private communications.
- Cross-border cybercrime requires separate consideration of criminal jurisdiction, banking jurisdiction, matrimonial jurisdiction and evidence jurisdiction.
- In a serious cyber-fraud case, the first few hours can matter enormously. Prompt reporting may improve the practical possibility of stopping further movement of funds and preserving evidence.